I’m really glad I had the chance to meet you during the training, and I wish you continued success.
武士道
鬼の道
義
闘志
侍
忍
斬
魂
武
心
PROFILE: SECURITY_RESEARCHER FOCUS: OFFENSIVE_SECURITY EXPERIENCE: CTF_AND_LAB_RESEARCH STATUS: OPEN_TO_OPPORTUNITIESPROFILE: SECURITY_RESEARCHER FOCUS: OFFENSIVE_SECURITY EXPERIENCE: CTF_AND_LAB_RESEARCH STATUS: OPEN_TO_OPPORTUNITIES
00// THE_MISSION
OFFENSIVE SECURITY RESEARCH
Building controlled, measurable security research around web, mobile, cloud, and red-team tooling. The focus is practical exploitation, clean documentation, and safe lab replication.
View Research Archiveroot@nyx0r:~$ whoami
Systems & Biomedical Engineering fresh graduate at Cairo University. Offensive security focused on penetration testing (Infrastructure, Web/Mobile Applications).
Self-taught through CTFs and real-world hunting. Currently building SpideyC2 a custom C2 framework for red team ops.
Self-taught through CTFs and real-world hunting. Currently building SpideyC2 a custom C2 framework for red team ops.
root@nyx0r:~$ ./reveal_power.sh
> Offensive Security Engineer
> Back-End Developer
> Computer Geek
05// FEEDBACK
WHAT THEY SAY
اجمد هكر ع الكوكب 💥❤️
It’s great seeing your dedication paying off wishing you more good moments like this ahead
الشغل معاك على مدار سنتين من أريح التجارب اللي عشتها لأنك بتجمع بين ميزة نادرة وهي إنك بتسمع وتفهم اللي قدامك بجد وبتضيف رأي مفيد يفرق في الشغل بمرونة ومن غير أي عند فبتخلي الشغل مريح وممتع وناجح في نفس الوقت وبتريح أي حد شغال معاك
01// LATEST_BLOG
LATEST WRITEUPS
Featured#MOBILE#OWASP
Android Hacking Lab Challenges Walkthrough
Breaking ten intentionally vulnerable Android apps with memory forensics, injection, path traversal, deserialization RCE and JWT theft
Featured#SECURITYRESEARCH#MYTHICC2
Evading Network Security Measures with Discord as an External Redirector
Research Notes: Exploring Discord-based redirection workflows with MythicC2
02// RECENT_PROJECTS
ARSENAL GRID
In Progress
SpideyC2 (Command & Control)
Developing SpideyC2, a custom Command & Control framework for centralized and secure management of remote agents, Supports encrypted communications, remote command execution, and Obfuscated Payloads Generation.
C\C++PythonEncryptionNetworking
Completed
Firmware Reverse Engineering using AI
AI-assisted reverse engineering of AVR firmware using Ghidra MCP and Claude AI to convert disassembled assembly code into readable C source code and recover program logic.
GhidraAI/MLReverse Engineering
View Project →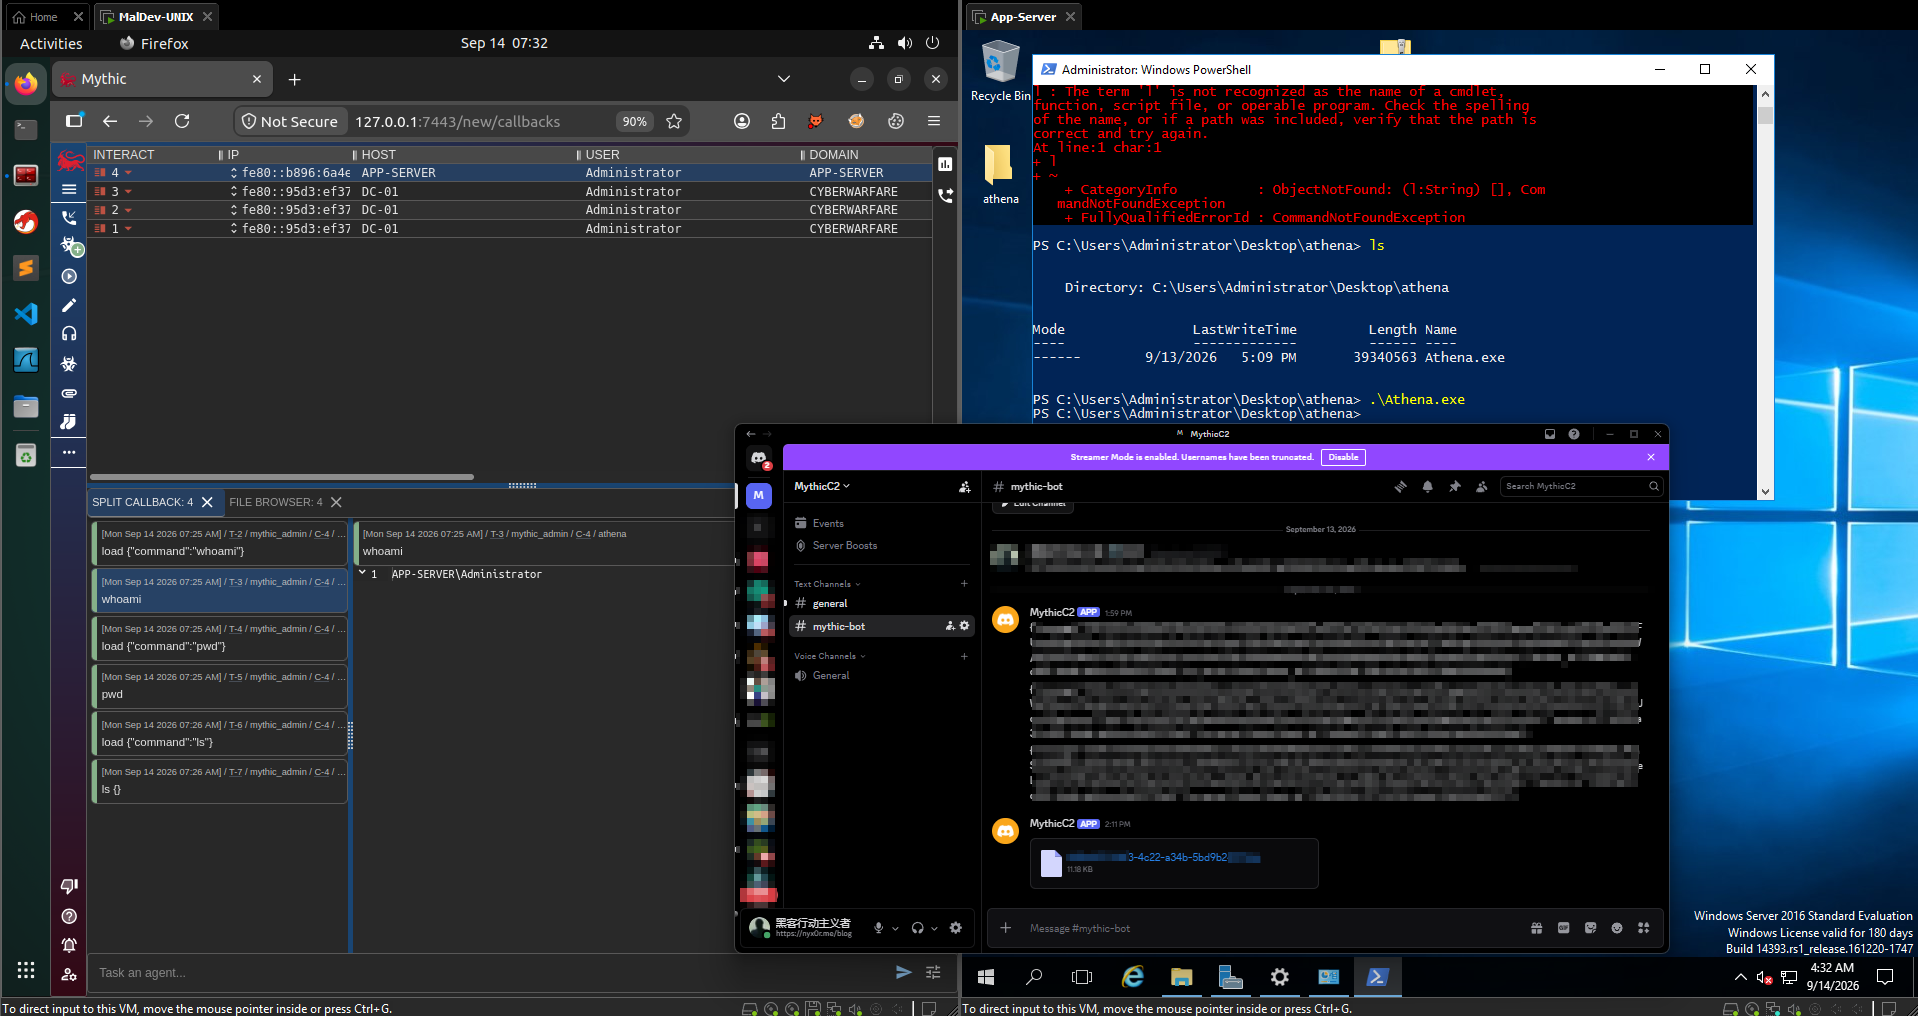
Continuous
RedTeam Attacks Replication
Built a self-hosted Active Directory lab to replicate real-world Red Team attacks by executing end-to-end TTPs, including information gathering, phishing, initial compromise, privilege escalation, and lateral movement.
Active DirectoryWindowsSecurity
Completed
Email Spam Detection
Email spam detection ML projects use machine learning algorithms to classify emails as spam or not spam based on content and features.
Machine LearningPythonNLP
View Project →
Continuous
PoCs & CTF Writeups
I am documenting and sharing my solutions to Capture The Flag (CTF) challenges and PoCs for public CVEs through detailed writeups on my portfolio & Medium & GitHub Account.
Security ResearchCTFDocumentation
View Project →03// CERTIFICATES
PROOF OF WORK
Verified
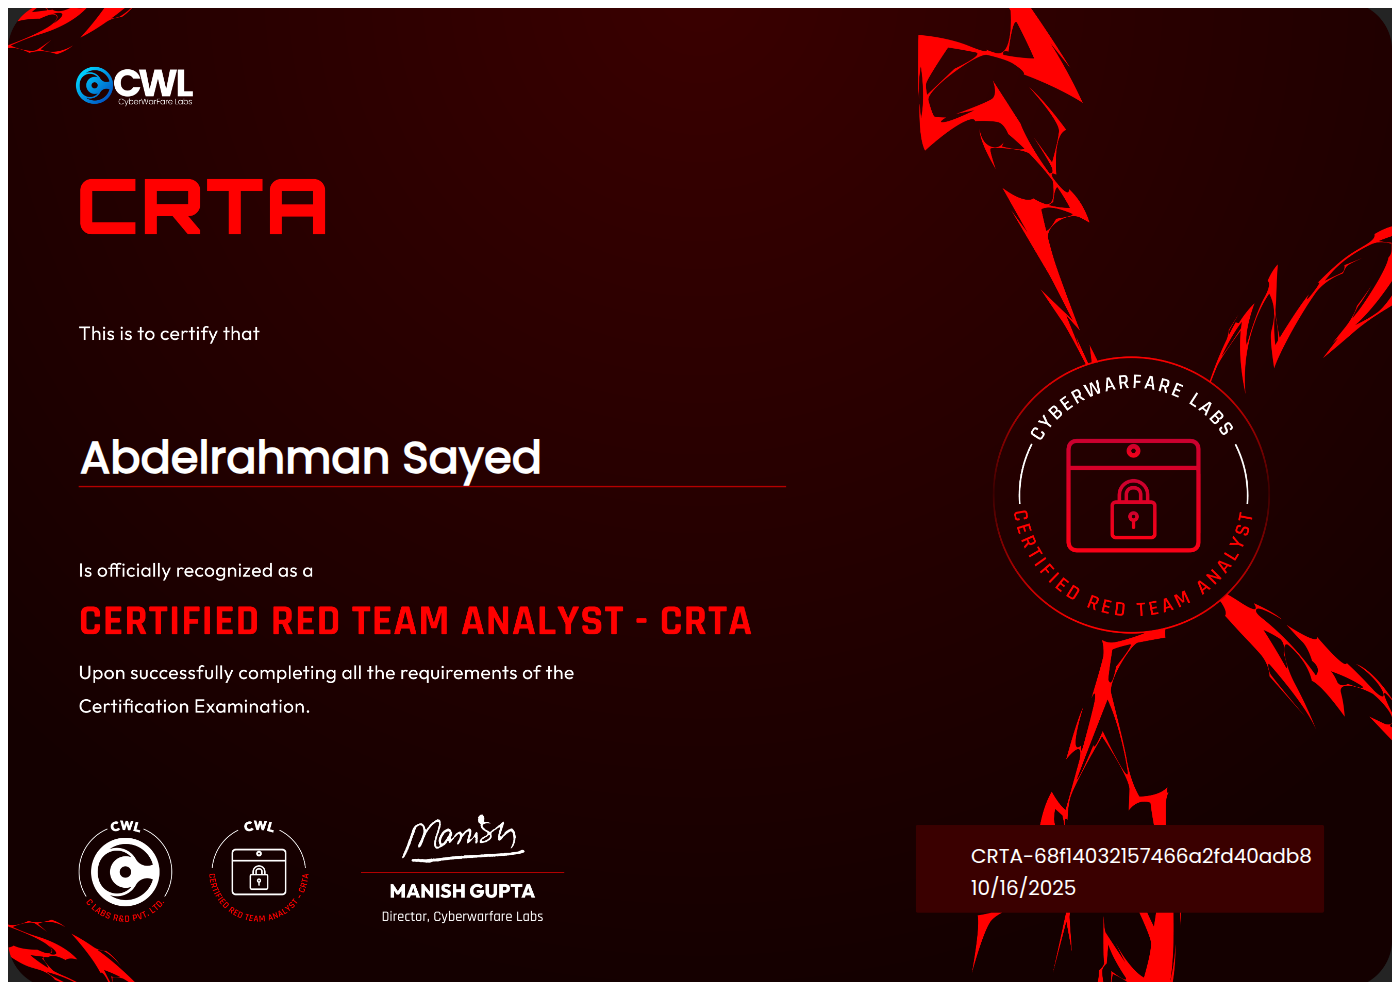
Certified Red Team Analyst (CRTA)
Cyber Warfare Lab (CWL)
Verified
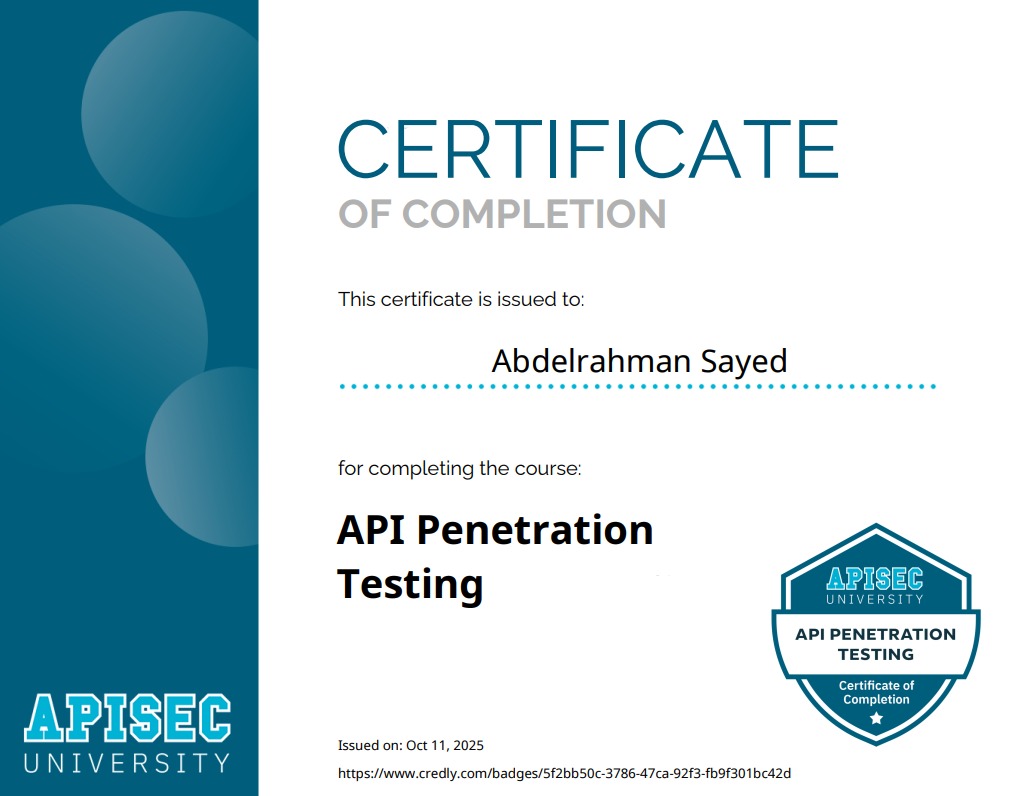
API Penetration Testing
APISEC University
Verified
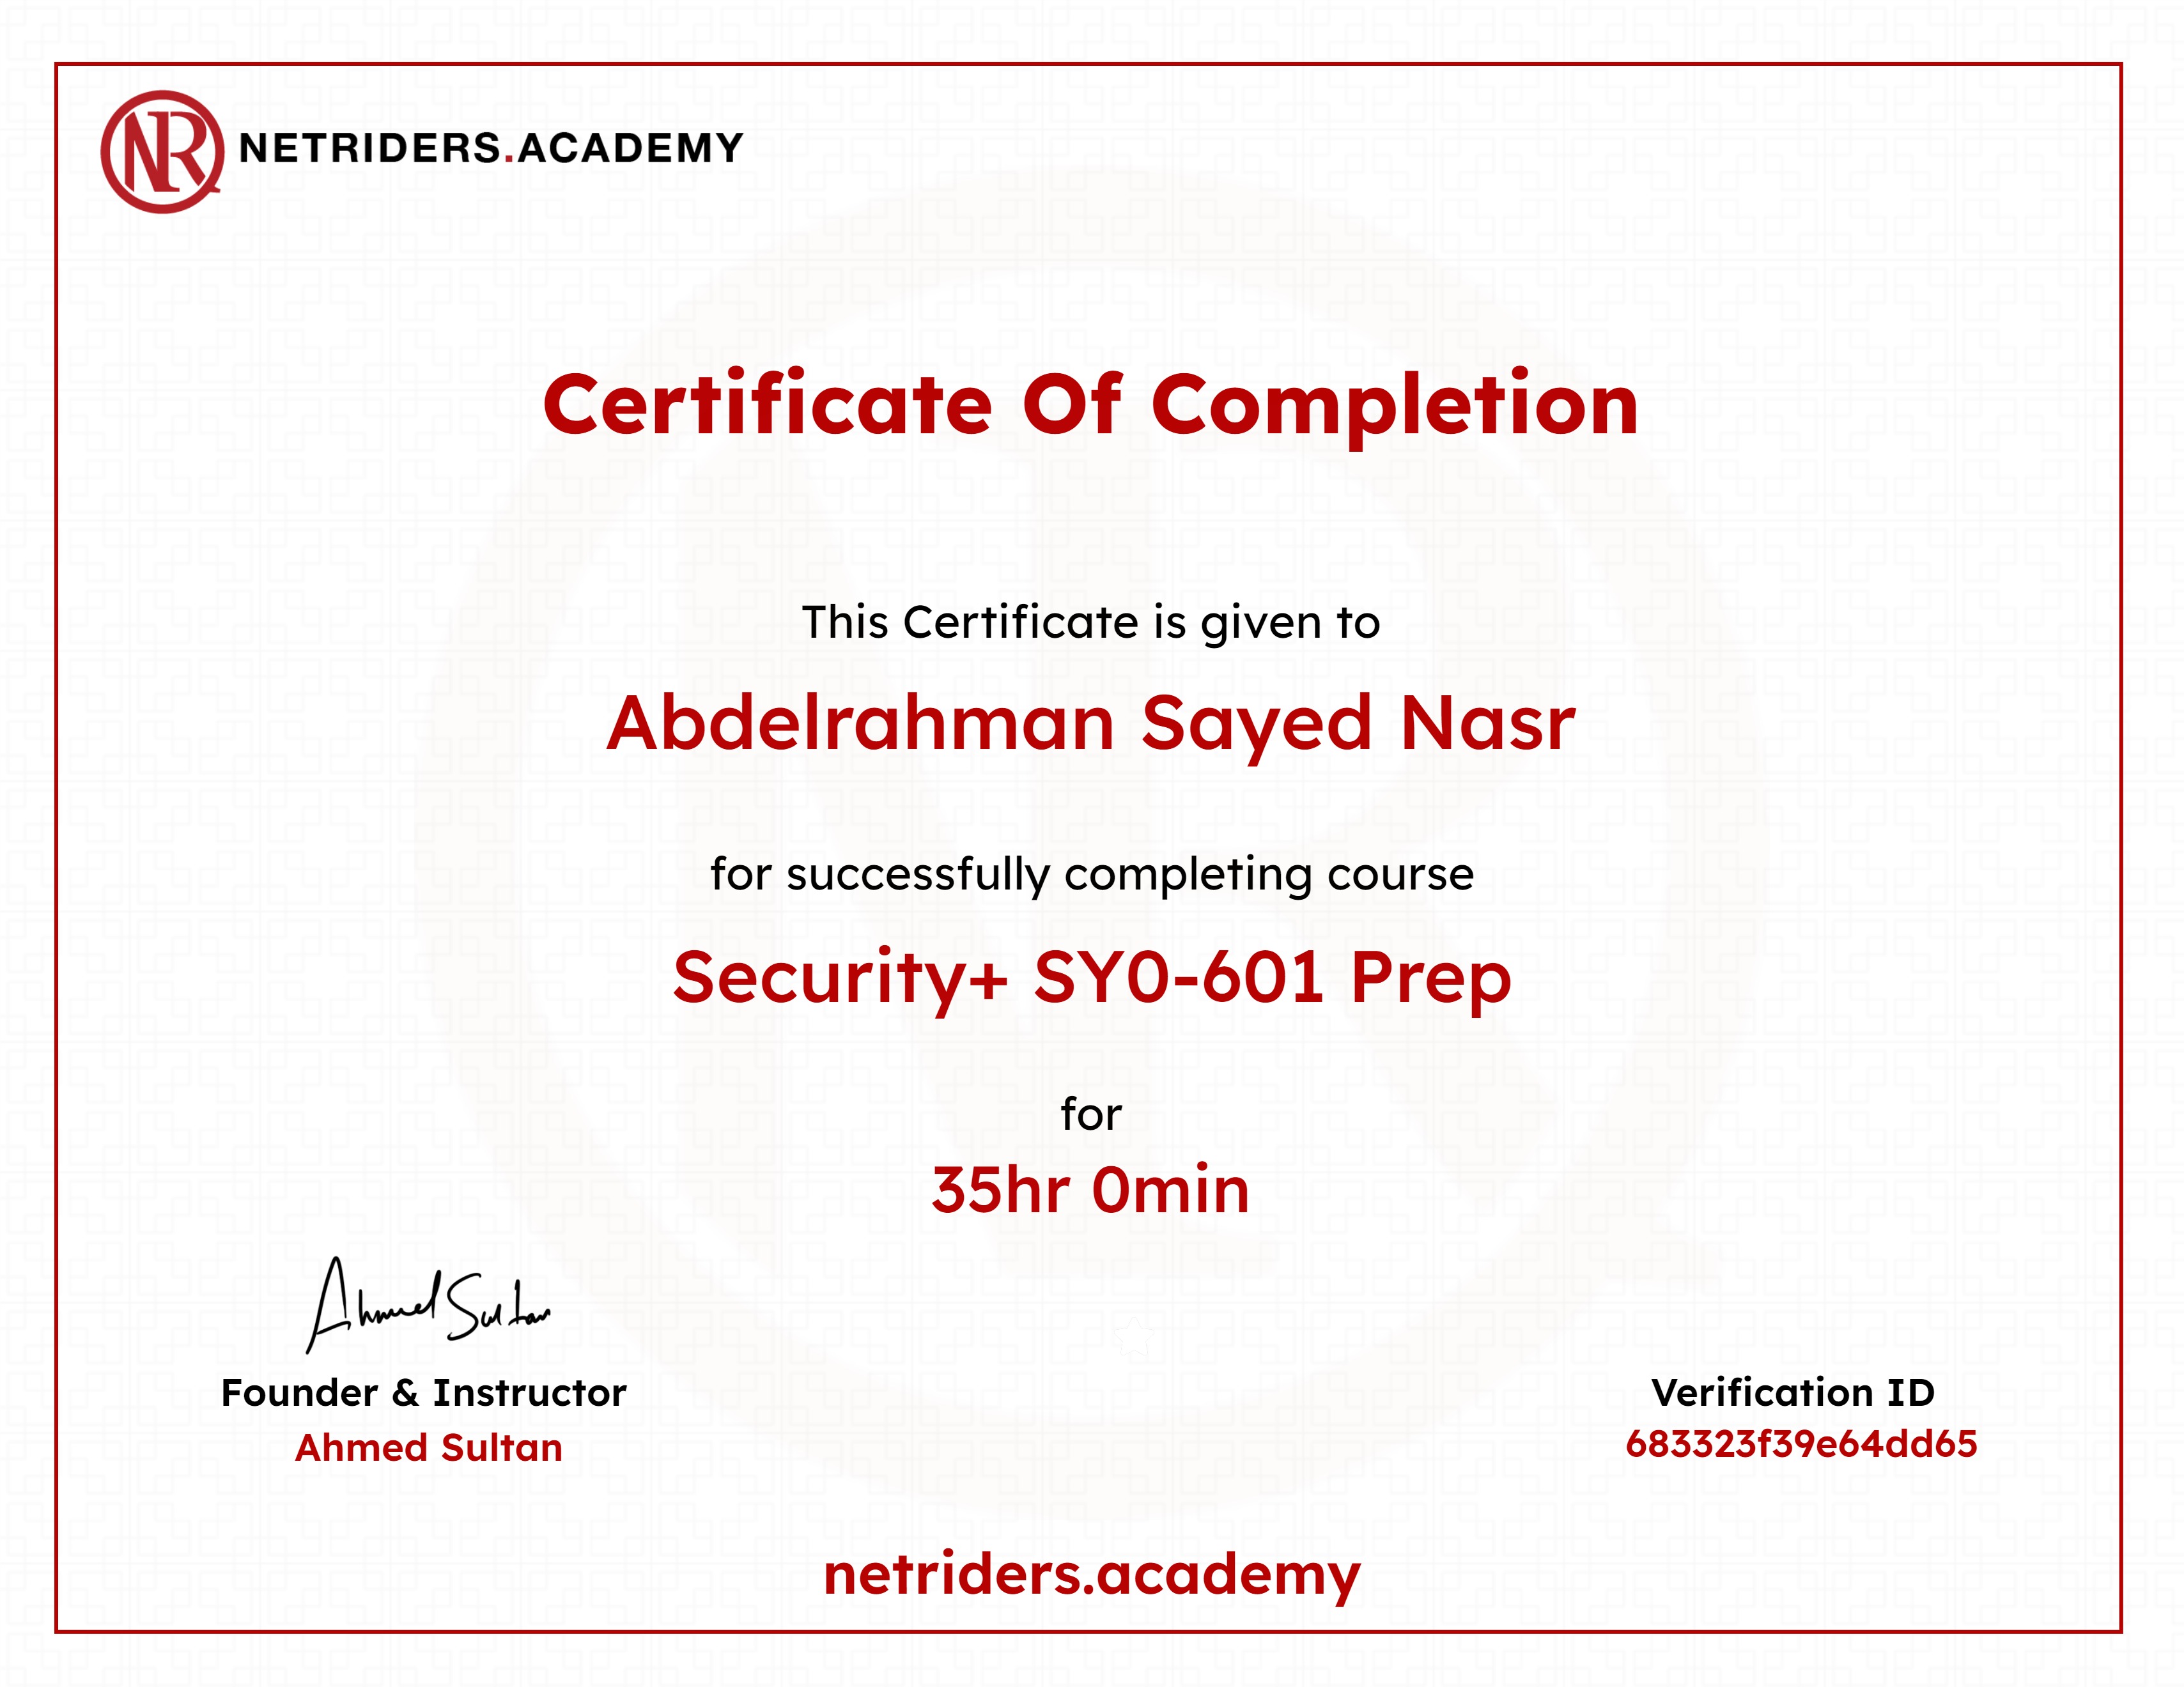
CompTIA Security+ Prep
Netriders Academy
04// EXPERIENCE
MISSION HISTORY
Aug - Sep 2025
Penetration Tester Internship
@ WE INNOVATE + ZeroSploit
Conducted security assessments, vulnerability testing, and exploitation techniques for web applications and infrastructure.
Aug - Sep 2023
Cybersecurity Trainee
@ Information Technology Institute (ITI)
Completed comprehensive cybersecurity fundamentals program including defensive and offensive security practices.
2021 - 2026
Systems and Biomedical Engineering Student
@ Cairo University
05// ESTABLISH_A_CONNECTION
LETS CONNECT
Always open to new opportunities, collaborations, and conversations about security.